
ICYMI: 35 Business Associations Call for Long-Term Reauthorization of CISA 2015
November 17, 2026
As Congress works to finalize the FY 2027 National Defense Authorization Act (NDAA), Business Roundtable and 34 other leading business and industry associations are urging lawmakers to include a 10-year reauthorization of the Cybersecurity Information Sharing Act of 2015 (CISA 2015) in the final conference agreement. In a letter to House and Senate Armed Services Committee leaders, the groups wrote:
“Over the past decade, CISA 2015 has become a foundational component of the nation’s cybersecurity. … The case for a long-term reauthorization has only grown more urgent.
“Recent incidents have demonstrated that advanced AI systems can identify and exploit software vulnerabilities at machine speed, collapsing the window between the discovery of a weakness and its use in an attack. … In this environment, the speed and breadth with which defenders share information determines whether they keep pace with adversaries. That speed depends on the legal certainty CISA 2015 provides.
“A long-term reauthorization of CISA 2015 is essential to our national security. We appreciate your leadership on this important issue and urge you to include these critical protections in the final conference agreement.”
The letter comes as the Roundtable ramps up its advocacy efforts in Washington, including meetings with members of Congress and staff, a full-page print ad in The Hill (see below), newsletter sponsorships in POLITICO Morning Cybersecurity and Axios Future of Cybersecurity, and digital advertising around POLITICO’s Decoded Summit.
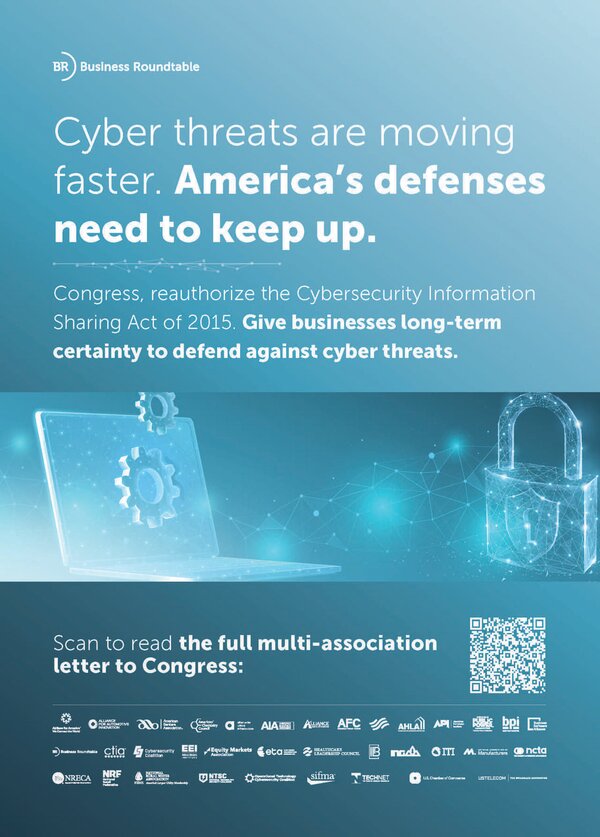
Photo: Business Roundtable Senior Vice President for Policy Matt Sonnesyn delivers remarks.
